Category Archives: General Security

Mind Maps about General Security Topics

Jasager with BackTrack 4 Mind Map

Jasager

After seeing some guys at Shmoocon 2010 with a neat Jasager BackTrack setup I thought I would go about creating a Mind Map on how to set this up.

So, I sat down with Robin Wood aka DigiNinja, the creator of Jasager for the day to go through how to set this up.

If you are new to Jasager be sure to read the original project pages to see what it can do.

Also, check out a recent Hak5 episode that shows Darren from Hak5 doing the Airport WiFi challenge.

This Mind Map takes you through how to create a cool Man in the Middle WiFi solution using a default install of both Jasager and BackTrack 4.

The Jasager responds to all WiFi probe requests and then the BackTrack 4 device allocates an IP address from its DHCP server and enables onwards routing to the Internet via a 3G modem or WiFi connection.
Jasager

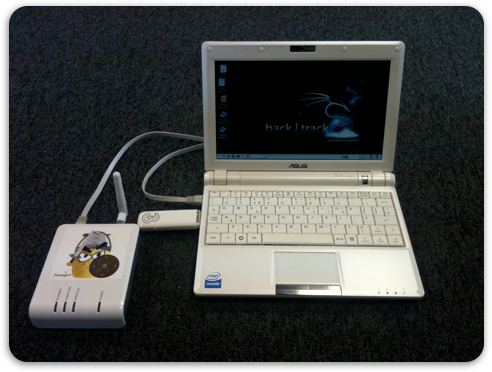
I built my solution using a Fon+ and an EeePC 900 running BackTrack 4. I have used both my 3G card and also my MiFi to provide onwards Internet. The solution works great and I have been able to do some fantastic demonstrations with this set up.

Click Here to Download the Mind Map and please let me now if you have any comments, good or bad.
Wireshark Network Analyzer Mind Map

Hot on the heels of my NetCat Mind Map I am happy to bring you my Wireshark Mind Map.

netcat mind map

Wireshark is the advertised as the worlds foremost network analyzer. It is provided as open source software and is therefore free to download and use.

Wireshark used to be called Ethereal and it is a tool I have been using for a number of years.

Sometimes, when troubleshooting, the ability to capture packets from the network and analyze what is going on is the only way to truly get to the bottom of an issue. There have been so many times when I have fired up Wireshark and fixed a network issue in a matter of minutes.

This really is a tool that you MUST learn how to use if you are involved in any network, security, or sysadmin role. The capture and display filters can be tricky to learn so persevere to get the tool to do what you want it to.

Take a look at the Mind Map and I also suggest you download Wireshark and get testing it on your own network.

I am already working on some more Mind Maps and they will be published soon.

NetCat Mind Map

It has been far too long since I last posted a Mind Map.

netcat mind map

I have recently started the Pentesting with Backtrack (PWB) online course from Offensive Security and I plan to sit the associated exam.

Therefore I thought it would be a great idea to create some more Mind Maps for some of the security tools covered on the PWB course.

So, here is my first of many Mind Maps.

This Mind Map is covering NetCat. NetCat is sometimes referred to as a network swiss army tool. It allows you to listen and redirect input and output to TCP and UDP ports.

Take a look at the Mind Map but the best way to learn this tool is to get a few machines hooked together and play.

Apologies for been away too long and I will ensure that I get some more Mind Maps online as they are created.

Configuring Secure Shell SSH on Cisco Devices

I have just been configuring SSH on some Cisco Routers so I thought I would Mind Map the process as I must admit it is a while since I have done it and I needed to think about the process.

As we all know, SSH should pretty much always be used when configuring Cisco equipment. In fact, I cannot think of any reason why you would not use it on a device which has the capability to be administered with SSH.

I still find core switches that have Telnet enabled and not SSH. Plucking the authentication passwords from the wire is child’s play, even in switched networks.

So, download and read this Mind Map and use it as an aid when you have to configure SSH on Cisco Devices.

Nmap Mind Map – General Security

Nmap Mind MapFor those of you who don’t already know, Nmap is one killer application for network security. Commonly known as a port scanner, Nmap will check for the existence of open ports on the given target machines.

Nmap has a lot more than just simple port scanning techniques and supports all of the common stealth scanning techniques such as the XMAS scan, FIN scan, NULL scan, and the RST scan. This provides a tool that can provides results you can rely upon.

One other area of use for Nmap is OS detection. Based upon various results, Nmap can quite accurately detect what Operating System the target machine is running.

I have been using Nmap for about four years and have considerable experience with it. It is a command line tool but it does have a graphical user interface (GUI) for Linux, OS X, and also Windows.

What I have prepared here, is a Mind Map that provides background information and a refresher about the types of scans Nmap can perform as well as explanations on what command line switches are required in order to run the associated scans.

You can download the Mind Map HERE.

Please let me know your thoughts.